The action proceeds unchanged
Policy resolved, the call is dispatched as written, and the decision is still recorded. An allow is evidence, not an absence of governance.
shapes no payloadPLATFORM / RUNTIME ENFORCEMENT
A wrong answer is a support ticket. A wrong action is an entry in a system of record. GovernorAI evaluates the call an existing agent is about to make and the action it then takes — at the seams the integration supports — and executes only the outcomes that seam can genuinely carry out. Everything else fails closed to deny.
Three outcomes end or suspend the call, and one lets it through. Allow is still a governed decision — it is recorded exactly like a denial.
THE OUTCOMES
Three of them stop or hold the action. Three of them change its payload. The difference matters, because a seam that can decide is not automatically a seam that can rewrite.
Policy resolved, the call is dispatched as written, and the decision is still recorded. An allow is evidence, not an absence of governance.
shapes no payloadThe target never sees the call. On the SDK path the wrapped function is never invoked and the caller gets the policy reason rather than a result.
shapes no payloadCarried internally as require_approval in audit and evidence, and delivered as pause at the SDK and HTTP boundary. On the Bedrock inbound path the proxy returns a 202 while the request waits.
Driven by the secret detector. Applied to request arguments and, on the seams that support it, to response bodies — JSON, plain text, and streaming bodies redacted in flight.
shapes the payloadDriven by the sensitive-data classifier and by structurally validated identifiers — payment-card numbers checked with Luhn, US social security numbers range-validated.
shapes the payloadRequest-side only. Argument narrowing reaches into JSON-encoded sub-fields of a tool call, and the narrowed arguments are re-verified against the exact payload actually sent upstream.
shapes the payload · request sideThe verdict comes from policy evaluation and deterministic detectors — regex, Luhn and range checks, keyword and path rules. An optional semantic detector exists, is off unless an operator enables it, can only add a deny to the strictest-outcome selection, and resolves a model error or timeout to deny.
policy + detectors, not inferenceEach verdict carries an explain code and a reason, and lands in the hash-chained audit ledger alongside the action context that produced it.
see Evidence & Compliance| Detector | What it catches | Resolves to |
|---|---|---|
| secret | Credential material — API keys, bearer tokens, JWTs and provider-specific key formats. | REDACT |
| sensitive_data | Regulated and confidential content, using the existing data-classification rule set rather than a forked one. | MASK at high and critical, approval at medium, allow below |
| regulated_identifier | Structurally validated identifiers the other two miss — payment-card numbers confirmed with a Luhn check, US social security numbers range-validated. | ALLOW · signal only, no rewrite |
| prompt_injection | Instruction-override attempts against the deterministic keyword floor. | DENY · signal only |
| encoded_payload | Base64 and hex runs that decode to printable text — the technique of smuggling instructions past a keyword filter by encoding them. Deliberately does not auto-block: a long printable base64 run is low-confidence evidence, because base64 is a common legitimate transport. It is surfaced as a detected type for a policy to gate on. | DENY · signal only |
| risky_tool_intent | Tool calls whose shape carries consequence a human should see before it lands. | APPROVAL · signal only |
| unsafe_destination | A destination argument pointing somewhere policy does not permit. | CONSTRAIN — the field is dropped |
| semantic_injection | Paraphrased or obfuscated instruction-override the keyword floor misses. Off unless an operator enables it, and it rides an existing model client rather than new infrastructure. | DENY · signal only · can only add a deny, never soften one · model error or timeout resolves to deny |
The seam capability registry is the load-bearing contract, not a marketing table: the inspector consults it at runtime and downgrades an unsupported outcome to deny, flagged as downgraded with an explain code suffixed _DOWNGRADED, so the product surfaces the downgrade rather than claiming the outcome that was asked for. A shaping outcome that rewrites zero fields is never reported as shaped either — it also fails closed. Redaction, masking and constraining apply where the seam supports them; allow, deny and approval do not touch the payload at all.
THE SEAM MATRIX
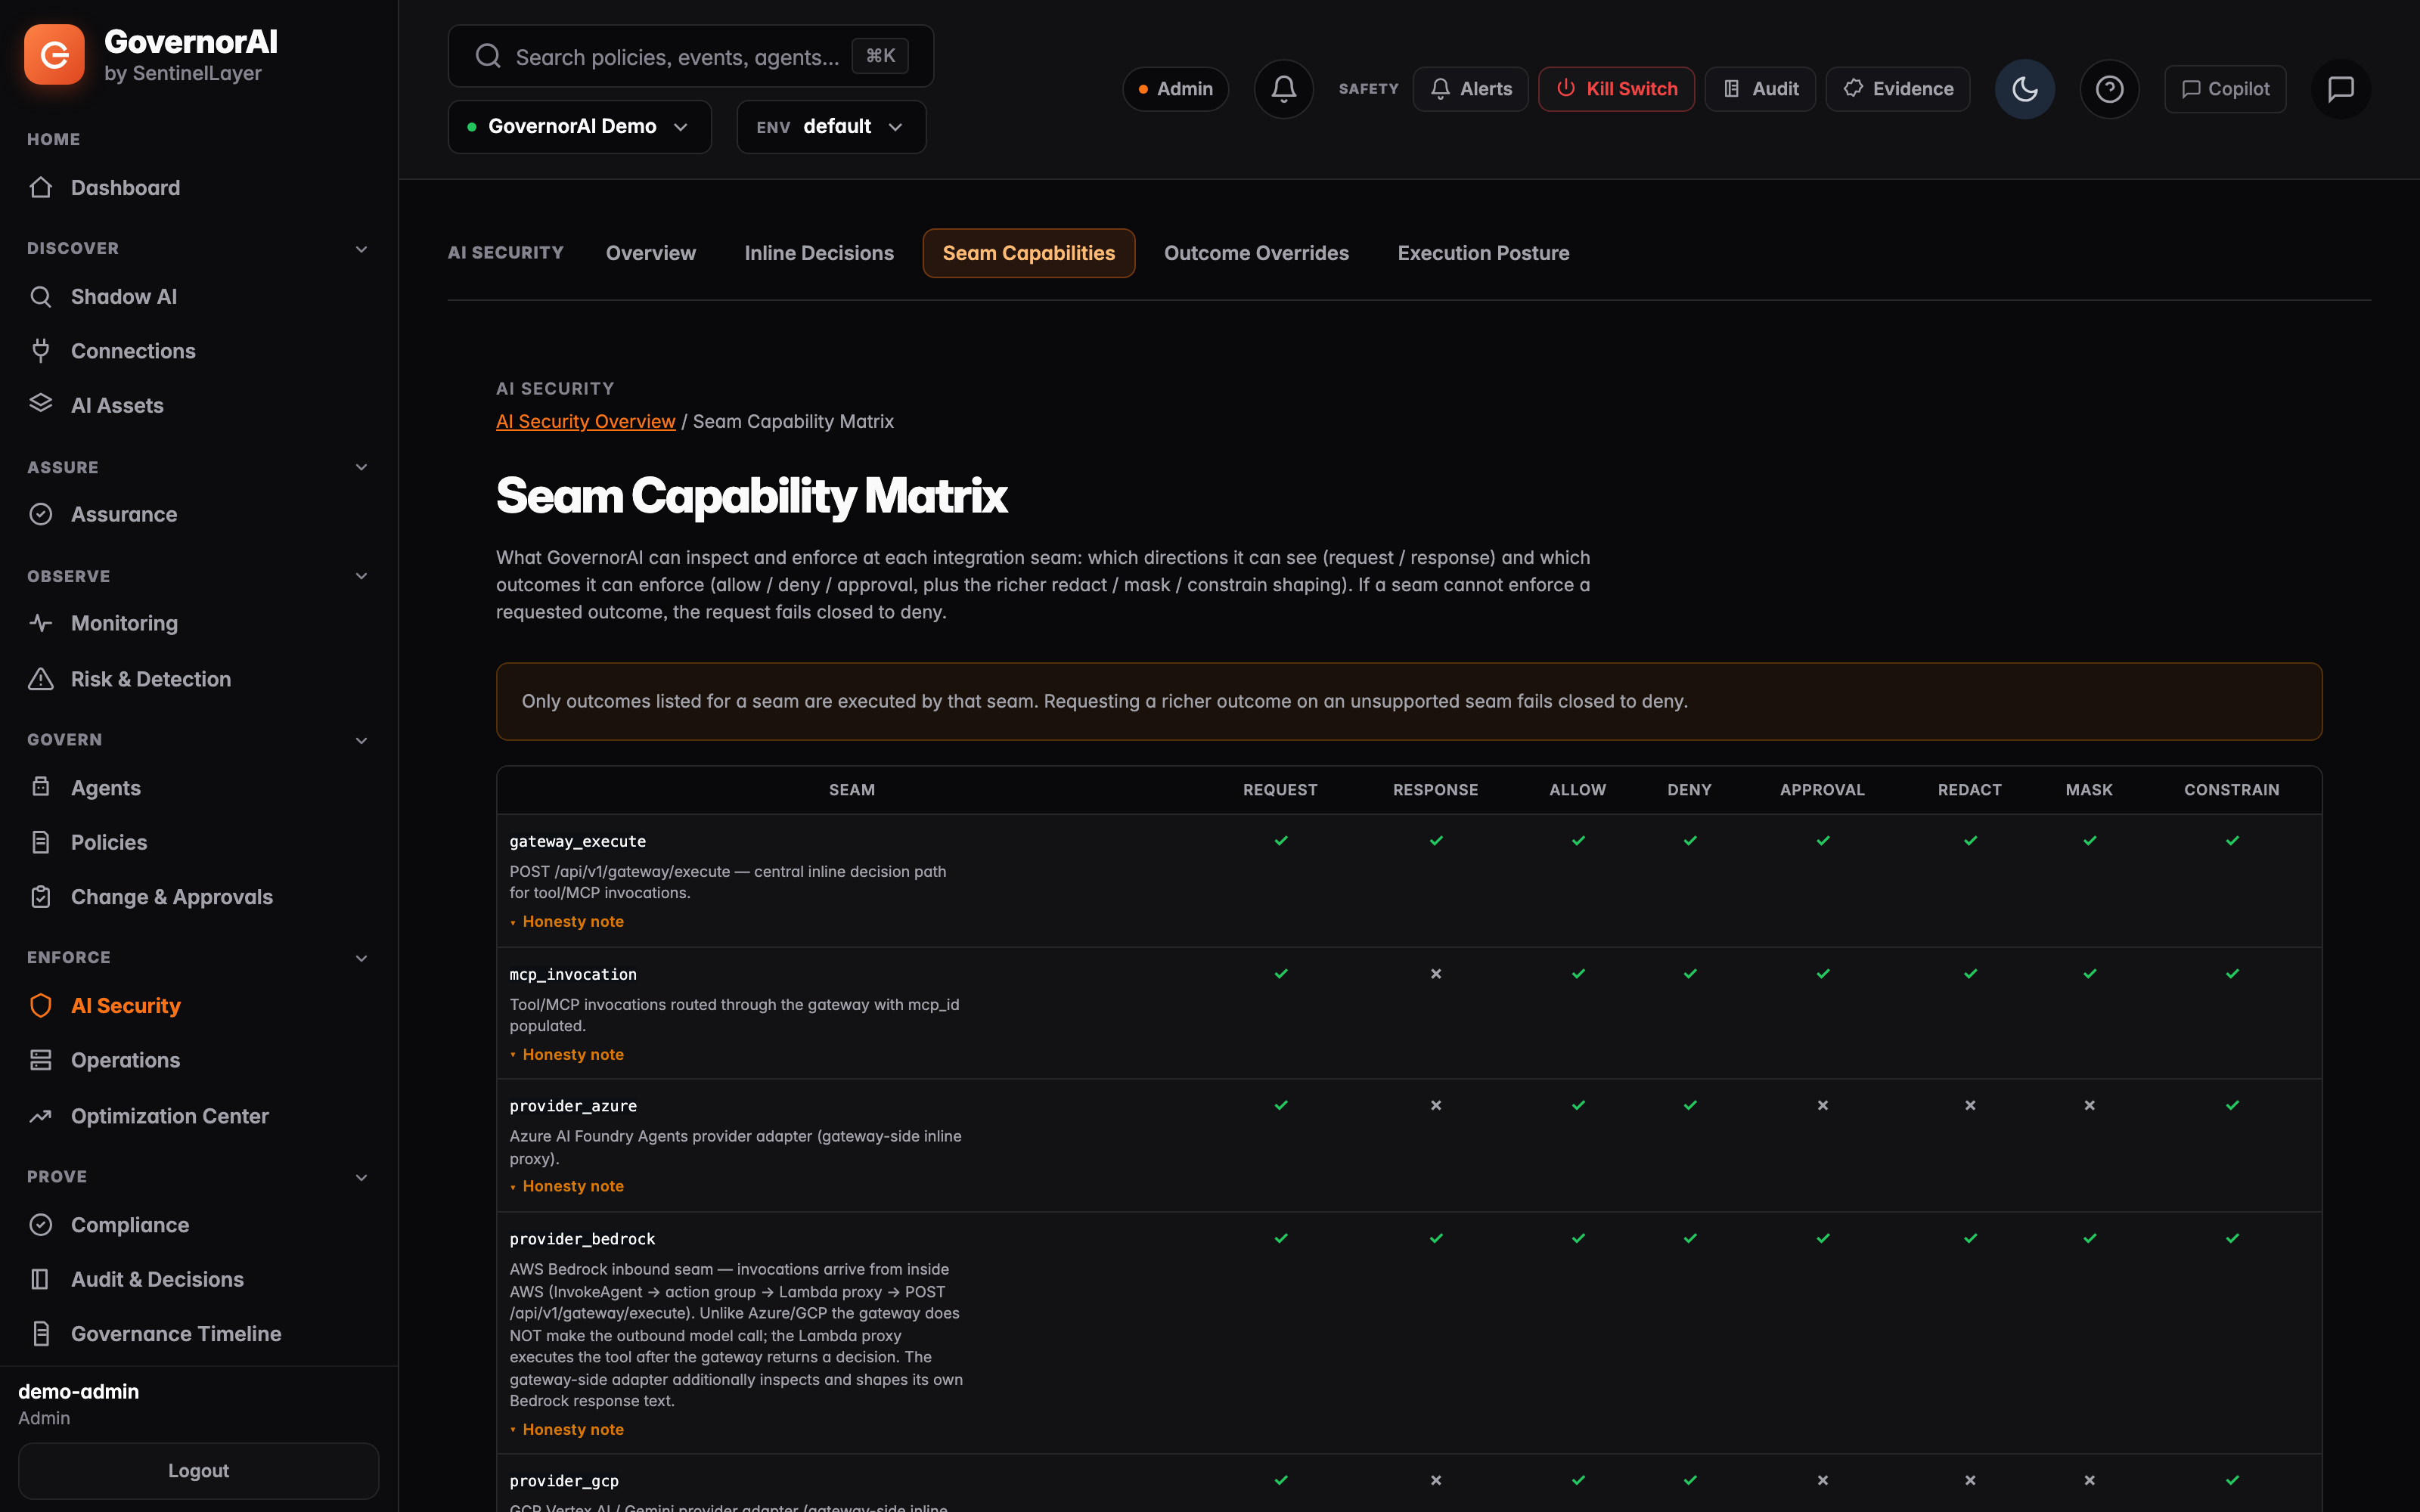
A seam is a code path where GovernorAI mediates an interaction. Each registered seam declares which interaction kinds it can inspect and which outcomes it can truthfully carry out. The product ships the matrix as a read-only API and shows it to operators — including the capabilities that are missing. Response inspection is real on two of these seams: gateway_execute shapes JSON, plain-text and streaming SSE bodies, redacting and masking in flight, and provider_bedrock inspects and shapes its own response text with the same re-scan proof before anything is returned.
FROM THE PRODUCT
The seam capability matrix, as it ships.All seven seams in one view, with request and response inspection and the six outcomes marked per row. Green ticks are capabilities the seam executes; grey crosses are capabilities it does not have, printed rather than omitted. Every row carries an honesty note explaining its boundary, and the banner above the table states the rule the runtime enforces.
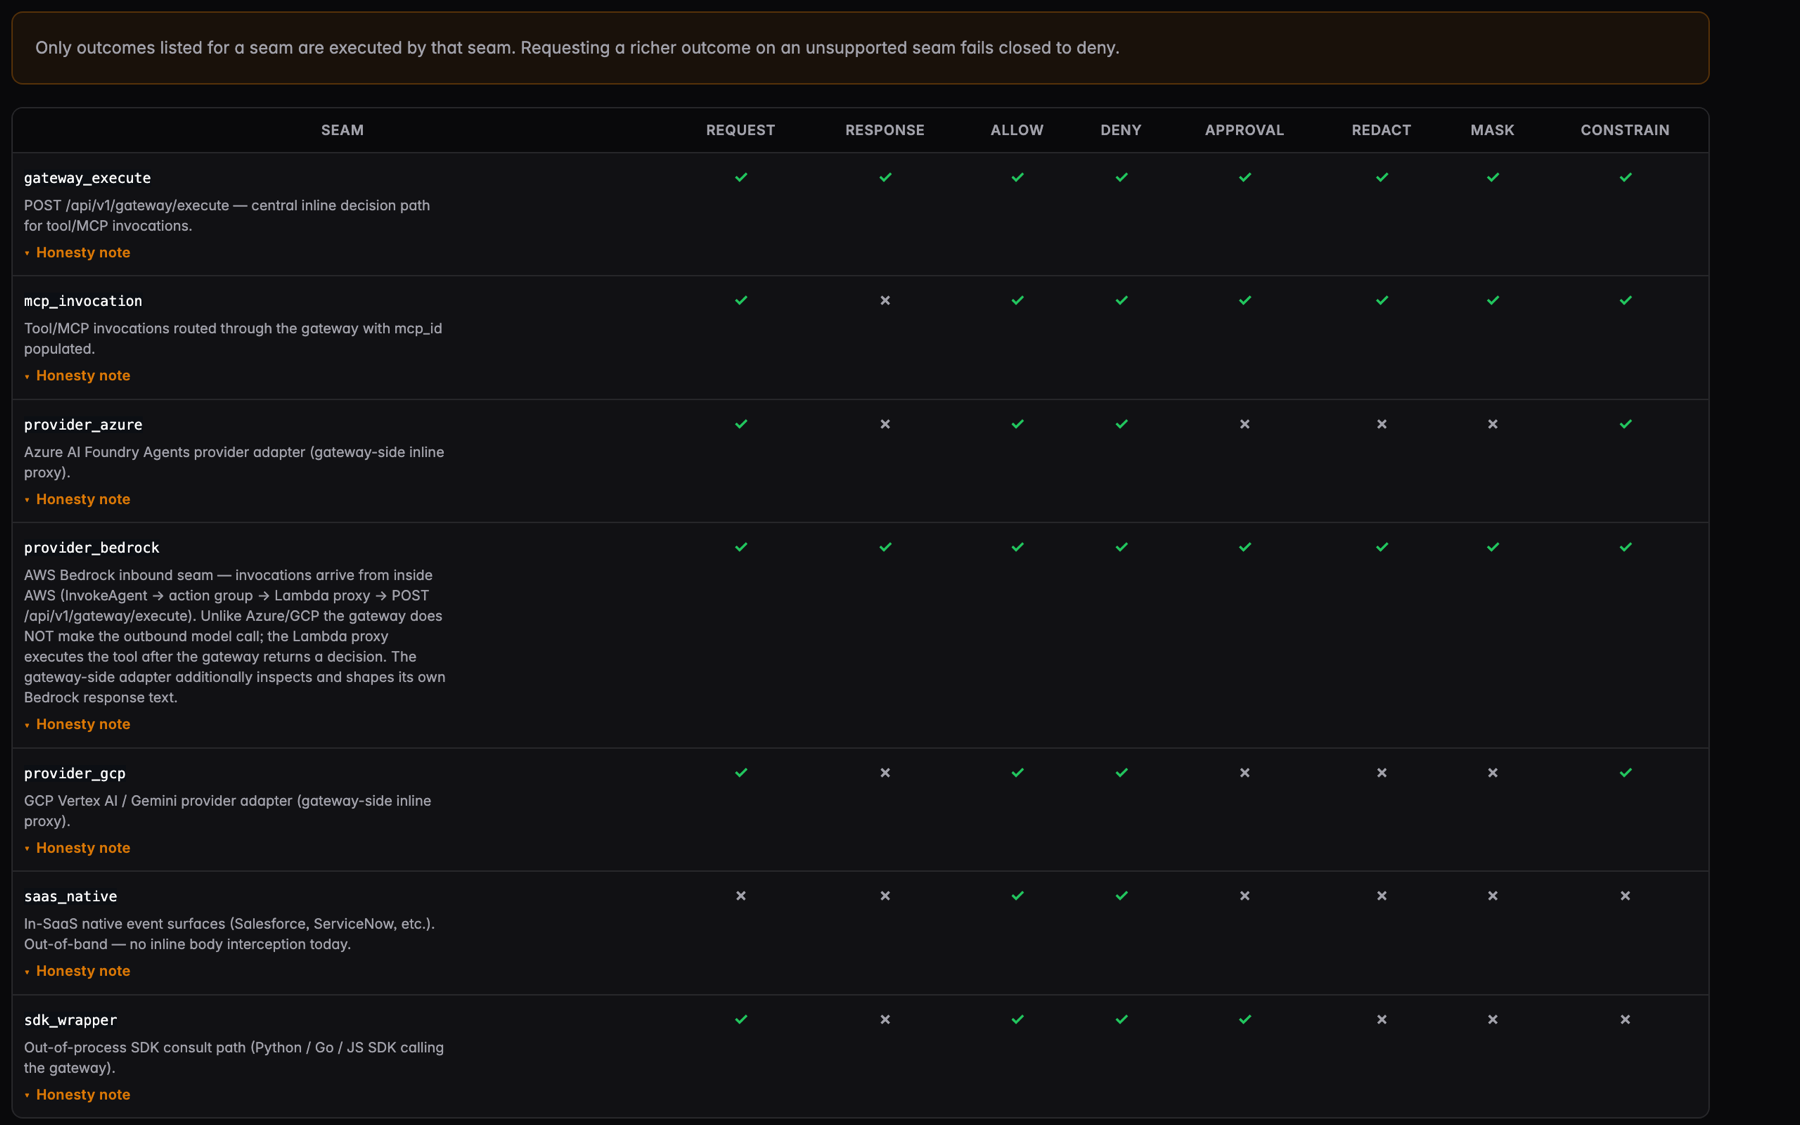
| Seam | What it mediates | Outcomes executed | Boundary |
|---|---|---|---|
| gateway_execute | The central inline decision path for tool and MCP invocations. Inspects prompts, tool arguments, response bodies and payloads, and treats a governed retrieval body as untrusted retrieved content. | allowdenyapprovalredactmaskconstrain | Shaping covers request arguments and response bodies, including JSON, plain text and streaming. When a response cannot be shaped safely — binary or non-text content, JSON that cannot be rewritten without corrupting it, or a sensitive value longer than the streaming inspection window — the seam denies rather than forwarding un-inspected data. Constrain is request-side only. |
| mcp_invocation | Tool and MCP invocations routed through the gateway with an MCP id populated. Argument-aware inspection runs even where prompt or response classification would be a no-op. | allowdenyapprovalredactmaskconstrain | Retrieval bodies an operator declared as a fetch are inspected as untrusted retrieved content for indirect injection. Ordinary model-answer responses are not inspected on this seam. |
| provider_bedrock | The AWS Bedrock inbound seam. Invocations arrive from inside AWS and the Lambda proxy executes the tool after the gateway returns a decision — the gateway does not make the outbound model call. | allowdenyapprovalredactmaskconstrain | Shaped arguments are verified against the exact payload sent to the proxy; a shaping that cannot be applied cleanly denies rather than sending a half-shaped request. The gateway also shapes its own Bedrock response text for content a detector can localize. Streaming, SSE and binary Bedrock responses are not shaped. |
| provider_azure | The Azure AI Foundry Agents provider adapter, as a gateway-side inline proxy over prompts and tool calls. | allowdenyconstrainapprovalredactmask | Request arguments can be constrained, and the constrained arguments are re-verified against the exact payload posted to Azure AI Foundry — a constraint that cannot be honored denies rather than forwarding an unconstrained request. Response shaping is not offered on this seam. |
| provider_gcp | The GCP Vertex AI and Gemini provider adapter, as a gateway-side inline proxy over prompts and tool calls. | allowdenyconstrainapprovalredactmask | Same boundary as Azure: argument narrowing is re-verified against the exact Vertex AI request and denies if it cannot be honored. Response shaping is not offered on this seam. |
| saas_native | In-SaaS native event surfaces — Salesforce, ServiceNow and similar. Out-of-band: GovernorAI ingests events but does not intercept the request body. | allowdenyapprovalredactmaskconstrain | No inline body interception, so no inline rewriting is claimed. A deny here is a downstream control action — a kill switch or a session revoke — not a request the seam edited on the way through. |
| sdk_wrapper | The out-of-process SDK consult path, where a Python, Go or JavaScript SDK asks the gateway for a verdict on a call it is about to make. | allowdenyapprovalredactmaskconstrain | The consult path returns a decision; it does not receive a shaped payload back. Shaping outcomes are therefore not advertised to SDK callers, and choosing one downgrades to deny. |
A cross in that matrix is a capability the seam does not have. It is printed, not omitted. saas_native carries allow and deny only, because in-SaaS event surfaces are out-of-band and nothing mediates the request body there. sdk_wrapper adds approval but shapes no payload, because the consult path returns a verdict rather than a rewritten body. provider_azure and provider_gcp constrain request arguments but are not offered response shaping. Ask a seam for an outcome it does not declare and the result is not a silent degradation to something weaker — it is a deny, marked as a downgrade, with the original request never dispatched.
A seam that is not in the registry falls back to allow, deny and approval over tool calls, MCP calls and prompts. No shaping outcome is advertised on an unknown seam, and choosing one downgrades to deny. Adding an outcome to the matrix requires shipping the runtime that executes it first — the registry is written from what the code does, not from what the roadmap intends.
GATEWAY INSERTION
Drop the decision into the MCP or API gateway you already run. Each adapter is a thin protocol translator: it parses a tool call off the wire, builds the canonical execute request, and asks the gateway for the verdict. There is one decision brain — policy, data controls, injection deny, approvals, kill switch, hash-chained evidence — and these adapters never re-implement it.
A gRPC external processor for Envoy Gateway, Istio, Gloo, Envoy AI Gateway and agentgateway. Allow continues, redact becomes a body mutation, approval returns 202, deny returns 403.
failure_mode_allow must be falsePoint the MCP client's server URL at the proxy. tools/call is governed; initialize, tools/list, ping and notifications pass through untouched. Allow forwards, redact rewrites the call arguments, approval and deny return a JSON-RPC error.
NGINX auth_request, Traefik ForwardAuth, an AWS Lambda authorizer, Apigee, Azure API Management. Allow returns 200; approval and deny return 403. A JSON verdict mode returns the decision and shaped arguments for guardrail webhooks.
A Portkey bring-your-own-guardrail webhook and a LiteLLM custom guardrail govern the model call itself. Our endpoint answers with an explicit negative verdict rather than a 5xx, because those hosts treat a server error as pass.
govern the call, not the keys# The identity travels in governor.* request headers:
# x-governor-agent-id · x-governor-org-id · x-governor-mcp-id · x-governor-tool
http_filters:
- name: envoy.filters.http.ext_proc
typed_config:
grpc_service: { envoy_grpc: { cluster_name: governor_extproc } }
processing_mode:
request_header_mode: SEND
request_body_mode: BUFFERED
failure_mode_allow: false # REQUIRED — fail closed if the processor is unreachableForward-auth cannot rewrite a body: the auth_request pattern has no body mutation, so that adapter is allow, deny and approval only. It emits a X-Governor-Shaping-Required header so the operator knows a redaction was requested and did not happen — use ext_proc or the MCP proxy when the payload must actually be rewritten. End-to-end redaction on an inbound self-execute caller also depends on the gateway returning shaped arguments, which it materializes for the Bedrock seam today; until that is generalized, ext_proc and the MCP proxy enforce allow, deny and approval end to end. And third-party hosts have their own defaults: Portkey's guardrail webhook fails open on timeout, and LiteLLM's post-call hook on streaming is audit-only. Our endpoint always fails closed; the gateway-side hook must be configured to treat a webhook error as a deny, and that configuration is yours to verify per deployment.
THE ARCHITECTURAL SPINE
An enforcement point that lets calls through when it is confused is a logging product with extra latency. Every path here resolves an unresolvable situation the same way: deny, with a reason, recorded.
| Condition | Resolution | Why |
|---|---|---|
| Gateway unreachable | DENY | A transport error is not an answer. The adapter synthesizes the deny and marks it as fail-closed so it is distinguishable in logs from a genuine policy deny. |
| Decision timeout | DENY | The decision client carries an explicit timeout, five seconds by default and configurable per deployment. Expiry resolves to deny, never to allow. |
| Non-2xx response | DENY | The gateway returns 200 for every real verdict, including deny and approval. So any 4xx or 5xx is an error condition, and the body is not trusted to argue otherwise. |
| Unparseable response | DENY | If the verdict cannot be read it has not been received. |
| Unsupported outcome for the seam | DENY | The seam registry says this seam cannot execute the outcome policy chose. Downgrading to something weaker would be a silent lie, so the decision resolves to deny and is flagged as downgraded. |
| Shaping rewrote zero fields | DENY | A redaction that changed nothing is not a redaction. The applier returns the count of fields actually mutated so the gateway can refuse to label it as shaped. |
| Redaction fails re-scan | DENY | After a plain-text body is shaped it is re-scanned with the same detectors. If anything still fires, the body still leaks and is not forwarded. |
| Un-localizable sensitive content | DENY | Only detectors that can prove where a match sits contribute spans. A classifier that returns a verdict with no offsets cannot drive a rewrite, so a shaping outcome resting solely on it denies instead. |
| Streaming window exceeded | DENY | The in-flight shaper keeps a bounded overlap so a token split across chunks is still seen whole. When a flush could emit the prefix of an unbounded secret, or an event exceeds the safe buffer cap, the stream terminates rather than emitting raw bytes. The window is honest: it is not unbounded in-flight redaction. |
| Shaped payload cannot be verified | DENY | On the provider seams the shaped or narrowed arguments are compared against the exact payload about to leave. A mismatch denies rather than forwarding a half-shaped request. |
| Inspection bounds exceeded | DENY | The inspector walks arguments and payloads against a depth and field budget. A structure that exceeds it has not been inspected, and uninspected is not allowed. |
The posture is zero-trust in the ordinary sense: nothing is permitted because it arrived from a trusted network, an identity is required on every governed call, and the default answer to an unresolved question is no.
A read-only execution-posture surface derives, from real decision records, what was authenticated, which tenant the action was bound to, and what policy decided. It reports the credential mode as scoped_api_key rather than dressing it up, reports signed evidence as configured-dark unless the deployment flag actually says otherwise, and reports just-in-time authorization and brokered credentials as roadmap — never live.
AROUND THE SEAM
A per-call verdict is the core, but not the whole surface. These are the controls that operate on an agent, a tool, a session or a whole organization at once.
Activate against an agent, a tool, a session, a namespace, a policy or an entire organization. Activation runs through one service so it can never be invisible: the registry write, the cross-pod propagation, the domain event, the audit-timeline row and the webhook dispatch all happen together.
one activation pathThe inline sensitive-data detector reuses the existing classification rule set rather than forking one, so what the data-controls surface says is sensitive is exactly what the seam acts on.
shared rule setToken-bucket limiting with an in-memory implementation for a single node and a Redis-backed one for a fleet, behind one interface so the behavior does not change with the deployment shape.
in-memory or Redis-backedA cluster-side agent governs each outbound CONNECT tunnel at the host and port level by asking the same gateway for a verdict, then opens raw TCP forwarding on allow. It does not terminate TLS — the body stays encrypted end to end between the caller and the destination.
one decision per tunnel openOutbound requests to tenant-supplied URLs are checked at dial time against the actual resolved IP, refusing loopback, private, link-local and cloud-metadata ranges. Because the check runs at the moment of dialing, a hostname cannot pass validation and then re-resolve inward, and every redirect hop is re-validated.
DNS rebinding closedWhere a provider ships its own guardrail plane, policy is compiled and attached to it, and any divergence from the source policy is named rather than hidden. This complements the inline seam; it does not stand in for it.
see Policy & GovernanceGovernorAI operates on the body it already receives at a seam. It does not inspect packets and does not analyze raw TCP or TLS traffic; the egress agent deliberately does not terminate TLS, and records one decision per tunnel open rather than one per logical call inside that tunnel. Data controls and injection defenses reduce risk at the seam — they do not prevent every encoded, indirect or novel attack, and nothing here is a claim about the quality of what a model produces. Where a customer runs a network or traffic-level security product, this sits alongside it and answers a different question: whether this agent may make this call, with these arguments, under this policy.
THE CAPABILITY MATRIX
A note on the word. An enforcement point is the mediated control point between an agent's intent and the target system. It implements the PDP/PEP pattern of NIST SP 800-207: GovernorAI is the policy decision point — it evaluates the policy and returns a verdict — and the mediated integration is the policy enforcement point, executing that decision before the target system is reached. Neither component is both. The registry calls these seams, and that is the term used in the API values and the table below.
Every seam declares which interactions it can inspect and which outcomes it can truthfully carry out. The runtime consults this registry on every call — ask a seam for an outcome it does not declare and the result is a deny marked as a downgrade, never a silent fallback to something weaker. The product ships this as a read-only API, including the gaps.
| Seam | Inspects | Allow | Deny | Pause | Redact | Mask | Constrain |
|---|---|---|---|---|---|---|---|
| gateway_execute | tool call · MCP call · prompt · response · payload · retrieved content | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ |
| provider_bedrock | tool call · prompt · response | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ |
| mcp_invocation | MCP call · tool call · retrieved content | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ |
| provider_azure | tool call · prompt | ✓ | ✓ | — | — | — | ✓ |
| provider_gcp | tool call · prompt | ✓ | ✓ | — | — | — | ✓ |
| sdk_wrapper | tool call · prompt | ✓ | ✓ | ✓ | — | — | — |
| saas_native | out-of-band events — no body interception | ✓ | ✓ | — | — | — | — |
A dash is a capability the seam does not have — printed, not omitted. Response shaping on gateway_execute covers JSON and plain-text/SSE bodies, including streaming responses, redacted and masked in flight. Where a response cannot be shaped safely — binary content, JSON that cannot be rewritten without corrupting it, or a sensitive value longer than the streaming inspection window — the seam denies rather than forwarding un-inspected data. Shaped arguments are re-verified against the exact payload sent upstream; shaping that cannot be applied cleanly fails closed.
DETECTORS
Regular expressions, Luhn and range checks, keyword and path rules. Two of the eight inspect retrieved content — the indirect-injection case where hostile text arrives in a document the agent fetched, after your prompt review has already passed.
secretsensitive_dataregulated_identifierprompt_injectionencoded_payloadrisky_tool_intentsemantic_injectionunsafe_destinationIN THE PRODUCT